Exporting for your CAB auditor
CAB auditors accept the CCB CyFun Self-Assessment workbook as the submission artifact. ECP fills that exact workbook for you and, on request, bundles all linked evidence into a single zip.
Two outputs, one source of truth
- xlsx: the CCB v2026-02-20 workbook with your scores filled in. This is the file the auditor signs off on.
- zip: the same xlsx plus an
evidence/folder containing every linked artifact, wiki page, and integration breadcrumb, cross-referenced by comment in each row.
1. Get Audit in shape
The workbook carries the scores and evidence you see on Audit, so start there. Open Audit in the top navigation and work through what is still Evidence missing or Document incomplete before you export. The export matches your active tier (Basic, Important or Essential).
If you're unsure of the tier, your IT partner can confirm it.

2. Decide what to bundle
On Audit, click the ··· button next to Recalc maturity (Audit-time actions). Leave Include full audit bundle off for the workbook alone, or tick it for a zip with the evidence files (xlsx + linked artifacts + wiki pages as markdown). Then click Export Basic CCB workbook (the name follows your tier).
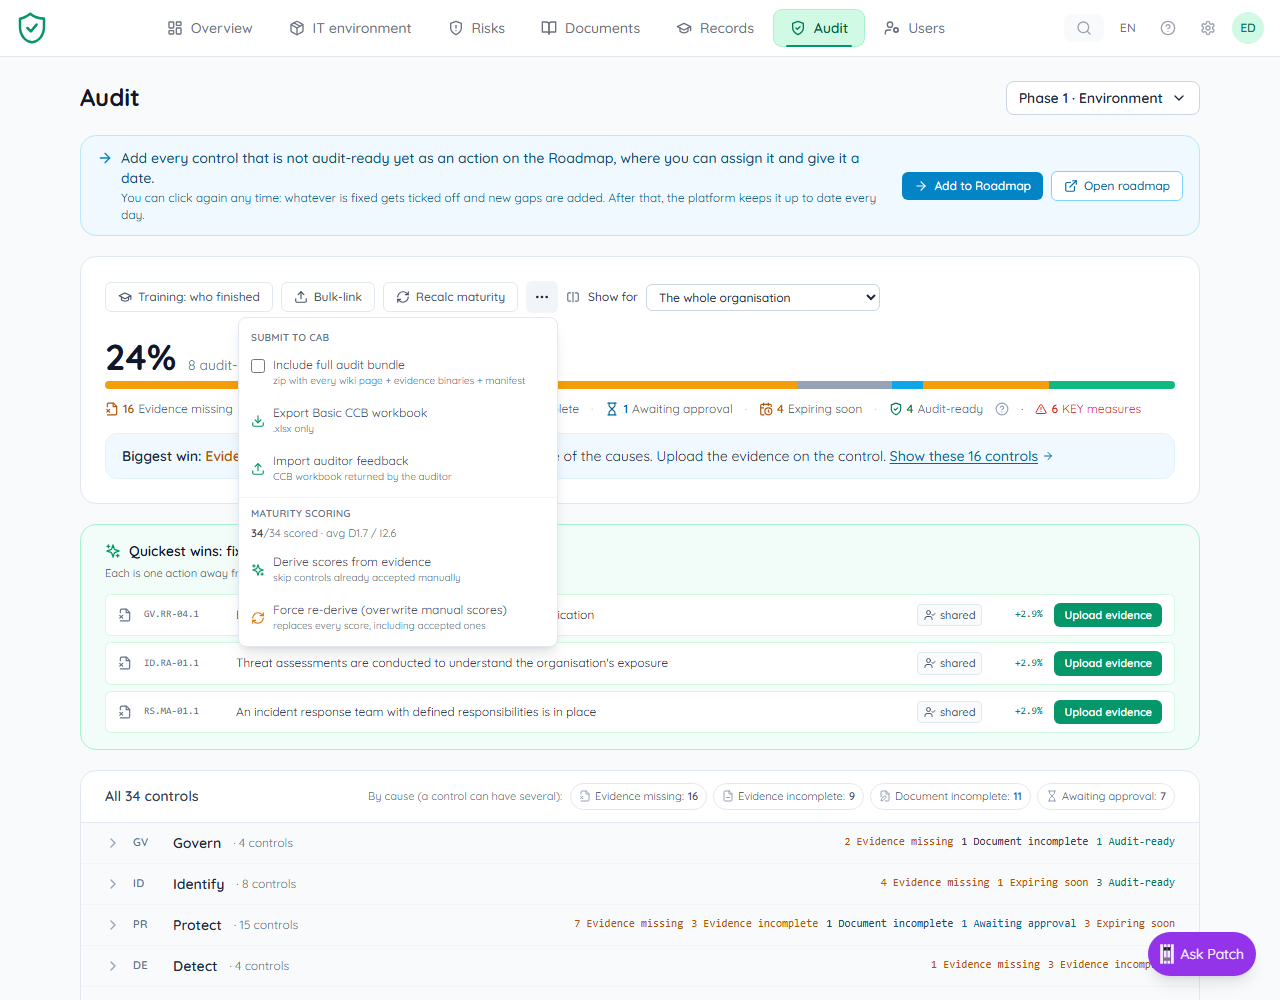
xlsx only
Use this when the auditor has their own access to ECP. Comments in the workbook link back to the control pages inside ECP, and the auditor clicks through to see live evidence.
zip bundle
Use this when you're emailing the file or uploading to a CAB portal. Comments point to local paths (evidence/CCB-REF/…) inside the zip so the auditor can open each artifact without ECP access.
The filename changes automatically: CyFun2025_Basic_YYYY-MM-DD.xlsx or .zip.
3. What's inside the zip
The bundle mirrors the structure a CAB auditor expects:
CyFun2025_Basic_2026-04-19.zip
├── CyFun2025_Basic.xlsx        ← the CCB workbook, scores filled in
├── README.md                   ← tier, export date, contents overview
└── evidence/
    ├── DE.AE-03.1/
    │   ├── siem-config-snapshot.png
    │   └── incident-response-procedure.md     ← wiki page as plain markdown
    ├── PR.AA-05.1/
    │   └── mfa-enforcement-log.csv
    └── PR.IR-01.1/
└── network-segmentation-diagram.pdf- → Wiki pages are exported as plain
.mdto keep the zip small (typical Basic tier under 20 MB) - → User-uploaded files (PDF, PNG, CSV, DOCX, …) keep their original bytes
- → Integration sources (Microsoft Graph, Sophos, Bitdefender, SentinelOne) export as a short breadcrumb
.mdfile naming the tenant and export timestamp - → External links (URLs you pasted as evidence) stay in the workbook as links, but they aren't copied into the bundle
4. Submitting to the auditor
Email the zip or upload it to whatever evidence portal the CAB uses. Include the README.md as a cover note: it lists the tier, export date, total byte count, and anything the auditor should know (missing evidence, unreferenced external links).
Your IT partner can also generate and send the bundle on your behalf from their Partner Dashboard.