#CyberWeekly
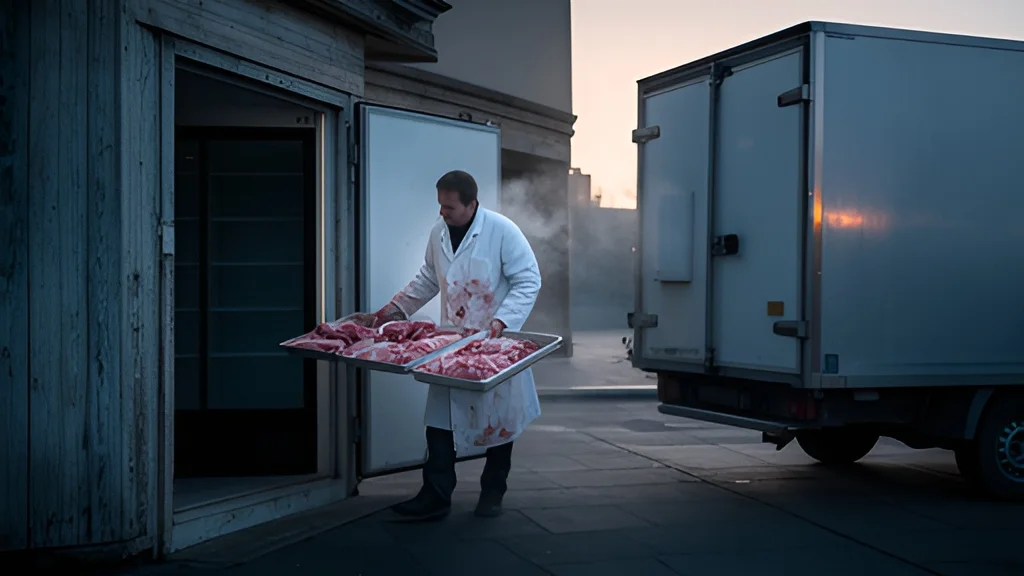
Warned three weeks ago. 60,000 euro of food gone on Monday.
This week in 30 seconds
- Belgian shops lost their freezers to a hacker, three weeks after the warning. Non-IT Get a written, dated line from your installer that the controller is off the internet and updated; name who answers the 3 a.m. alarm. IT Building controllers: not reachable from the internet, then firmware.
- Pluxee, the meal-voucher company, found an intruder on a server. Non-IT Nobody gets a PIN or password over mail, text or phone; second login step on the employer account.
- Four flaws hackers already use. IT WordPress core and Cisco VPN now; Ivanti again; old Macs this week.
- New in ECP, our platform that helps small firms and their IT partner put their cyber security in order: connect Claude or ChatGPT to your own compliance file, and six free templates for IT partners.
Non-IT Mail your cooling installer today. Ask one thing: "Can our controller be reached from the public internet, and does it run the current firmware? Confirm with the date." Until you hold that answer, assume it can be reached. Then write down who gets the temperature alarm at 3 a.m. and whether they can switch the system to manual.
IT The installer's word is not enough this week. Check from outside the building: does the controller's web page answer on a public address? If it does, that is tonight's job, patch or no patch. Danfoss, Copeland and Dixell rows are in Patch Watch.
Is this your problem? Yes, if a machine in your building has a web page. The supermarkets were hit because their freezers answer to the internet. The same controllers run cold rooms in butchers, bakeries, pharmacies, restaurants and flower shops, and the same logic runs your heating, your solar inverter and your door badges. NIS2, the EU cyber law, does not come into it; a freezer at 15 degrees does.
What happened In the night of Sunday 1 to Monday 2 November someone switched the cooling in dozens of Belgian shops to defrost, over the internet. More than 40 Delhaize shops, mostly franchised Shop&Go and Proxy stores, 15 Carrefour shops, a handful of Spar and Intermarché stores, IKEA in Mons, and at least two butchers (VRT NWS liveblog).
- The damage: at Proxy Delhaize in Hoepertingen the freezers stood at 15 degrees instead of minus 22. The owner estimates at least 60,000 euro of food thrown away. In Eeklo the freezers had been set to 50 degrees. A butcher in Hove lost several hundred kilos of meat.
- The one that got away: butcher De Laet & Van Haver noticed at around 3 a.m., paused the system and kept the damage small. Same attack, one person awake, a fraction of the loss.
- The law: food that went above the limit, 7 degrees for the fridge, 5 for meat and fish, minus 18 for frozen, may no longer be sold, says the food agency FAVV. Warm stock is a write-off by law, not a judgement call.
- How: Sabcobel, the installer behind many of the hit shops, says the evaporators were switched to defrost remotely through store controllers that were reachable from the internet. Both Sabcobel and Danfoss had told clients to secure or disconnect them. A small number had not.
- Who: on Wednesday a pro-Russian group claimed the attack on Telegram, along with 2,500 lines from a Danfoss database including logins. Neither claim has been verified. The federal prosecutor opened a criminal investigation on Monday. Shops in Sweden, the Netherlands, Luxembourg, Ireland and Finland were hit the same way.
Why this one is different from week 42. Three weeks ago the story was a flaw and a precaution: Delhaize pulled its own plug before anyone attacked. This week the attack ran, in Belgium, and the dates are the story. Warning from the CCB, Belgium's cyber security centre: 14 October. Fix available: for over a year, says the CCB. Shops hit: 2 November. A year to patch, three weeks of warning, and on Sunday night a small number of controllers still answered to the internet.
The one thing: by tonight you hold a dated, written line from your installer, or you know that you do not.
Three things to do this week:
- Non-IT Ask in writing, read the answer. The sentence at the top of this story, by mail, to the firm that services your cooling, heating or doors. A spoken "yes, that is fine" is what the hit shops had. If the installer cannot answer, that is the answer: ask them to take the controller off the internet until they can.
- Non-IT Name the 3 a.m. person. Who gets the temperature alarm, by text, app or phone, and can that person switch the system to manual? That is the difference between the butcher who noticed at three and the shop that found out at opening time. If the alarm goes to nobody, you are the second shop.
- Non-IT Call your insurer this week. Ask whether stock lost because someone changed a setting from outside is covered, and under which policy. We do not know the answer for your policy. Many stock policies cover a failed compressor and say nothing about a hacker. Get that in writing too.
IT Check from a public address, not from the shop Wi-Fi. The CCB also says a factory reset is not enough while the device stays reachable; the fix is the network, then the firmware. Our guide on supplier access covers the written agreement with the installer.
Three weeks' notice. Whether your installer read it is this week's question.
VRT NWS liveblog: supermarkets and butchers hit by a cyberattack on their cooling (2-4 Nov 2026) →
Patch, our house bot, writes:
"I was not in the freezer aisle on Monday. I read the liveblog like everyone else, and then I read the CCB warning of 14 October again. It is a good warning: take the cooling controllers off the internet, the fix has been out for over a year."
"It has one gap. It is written for installers and IT people, and in a shop with twelve staff nobody reads the CCB. The person who finds out it was not read is the one holding the mop at opening time, with the thermometer at fifteen."
"So, my one thing: do not wait for the installer to read it. Forward the warning yourself, today, and ask for a dated reply. That turns 'the installer' into a name with a date next to it."
— Patch, your friendly house bot
Pluxee found an intruder. Your card still works. Your inbox is the target.
Non-IT Tell staff today: no mail, text or call about their Pluxee card gets a PIN, password or card number, whoever is asking. Then put a second login step on the account that manages the vouchers for your company, usually HR or the bookkeeper.
IT Nothing to update. The employer account at Pluxee gets a second login step and a check that the password is not sitting in a shared mailbox. Mail filter: inbound mail naming Pluxee from outside pluxee.be gets a flag, the same recipe as last week's MyMinfin rule.
What happened On Monday 2 November Pluxee Belgium detected malicious activity on one of its servers. The company says an attacker may have had access to names, email addresses and phone numbers of cardholders. It does not say how many. It found no problems with payment integrity and no suspicious transactions, and the cards keep working (VRT NWS, ITdaily).
- What Pluxee told cardholders on Wednesday: stay alert for unexpected emails, text messages or phone calls, and "Pluxee will never ask you to share your PIN code or password".
- Why it is your problem: meal-voucher cards sit in a lot of Belgian wallets, so there is a fair chance some of your staff are on that list. The address file of a benefits company is a phishing list with the employer's name attached.
- Who gets the sharpest message: the person who orders the vouchers for your company. They hold a login to the employer portal, and a mail saying "your order could not be processed, log in here" lands on the busiest day of the month.
A leak is a forecast. Last week's story was 47 Belgian organisations that leaked data since January. This one shows what comes next: the company itself warns you that the fake mails are coming, before the first one arrives. That pattern, a leak followed by messages built from it, now has its own entry in our guide on spotting phishing.
And the tax office, one week on. The FOD Financiën says MyMinfin, Tax-on-Web and Biztax are back and safe to use since 31 October, and that no data was taken (FOD Financiën). The rule from last week's tax-office story stands: type the address yourself, never tap a link in a mail.
The card works. The call about the card does not.
VRT NWS: possible data leak at Pluxee, names and contact details of cardholders (4 Nov 2026) →
Platform Spotlight
Ask Claude or ChatGPT about your own compliance file
New here? Easy Cyber Protection (ECP) is the platform IT partners use to get small and mid-sized firms ready for a CyFun audit under NIS2.
If you already use Claude, ChatGPT or Copilot at work, you can now ask it about your own cyber file: "what is still open before our audit?", "which supplier has no written agreement?". The answer comes from your ECP file and links to the control it talks about, instead of a general guess. Your IT partner switches it on once under Settings, Connected AI apps (one address, pasted into the AI app). The app reads only the file you connected, and only after you approve it on an ECP page.
- It reads before it writes. Every app first sends you to an ECP approval page. The AI can fill one field, after you approve the exact value. It never publishes anything. A bigger change becomes a draft for a person to approve. Disconnect in one click, in the same settings page.
- Six free templates for IT partners. An incident response plan, a tabletop exercise kit with three scenarios, a supplier security questionnaire, an acceptable use policy, a board memo on NIS2 and CyFun, and the CyFun Basic evidence checklist. English, Dutch and French, behind the same email form as the other downloads.
- Also this week: every gap in the register now names the risk behind it, and Google Workspace users and devices land in the account register by themselves. The rest is in the changelog.
IT Connect Claude Code or Cursor with the one-line command on the help page and ask for the open work across a client before the monthly call. The supplier security questionnaire is the one to send to a cooling installer.
Non-IT Try it with the question you would normally ask your IT partner, and see whether the answer comes with a link to the control. The changelog lists everything that shipped this week.
Patch Watch
For your IT partner
Three weeks' notice: four fixes, the deadline per product
Not in IT? Forward this part to your IT partner and ask for a yes on each of the four rows.
IT Per product: the flaw, the fix, the deadline and who checks.
- Cooling, heating and access controllers (Danfoss, Copeland, Dixell)
Flaw: Danfoss AK-SM 800A, CVE-2025-41450 and CVE-2025-41451, authentication bypass, used this week against Belgian shops; Copeland xweb controllers also targeted.
Fix: not reachable from the public internet (VPN or internal network only), then current firmware, Danfoss "Strict" mode. The CCB says a factory reset is not enough while the device stays reachable.
Do by: tonight.
Who checks: IT, from a public address, in every client building with a cold room, a heating system or badge doors. - WordPress core
Flaw: CVE-2026-119977, race condition in the full-package core upgrade, remote code execution without login, exploited.
Fix: WordPress 7.1.4, released 28 October, backported to every line down to 4.7. Auto-updates are rolling out. Open the dashboard of each site and read the version number, do not assume.
Do by: now. CISA says 6 November.
Who checks: IT or the agency that runs the site. - Cisco Secure Firewall ASA and FTD
Flaw: CVE-2026-76418, CVSS 8.6, denial of service, exploited since October according to Cisco. Only firewalls with SSL VPN and secondary authentication in the tunnel group.
Fix: ASA 9.16.4.104, 9.18.4.96, 9.20.4.50, 9.22.3.200, 9.23.1.48 or 9.24.1.27; FTD 7.0.11, 7.2.13, 7.4.9, 7.6.7, 7.7.14, 10.0.3 or 10.1.1. No workaround; until then, disable the secondary authentication.
Do by: now. CISA's deadline was 1 November.
Who checks: IT. - Apple Safari and WebKit on older Macs
Flaw: CVE-2024-27834, on CISA's exploited list since 4 November.
Fix: Safari 17.5, released May 2024 for macOS Monterey and Ventura. A Mac that never got it is on an unsupported system; move it to a supported macOS.
Do by: this week. CISA says 18 November.
Who checks: IT, on every Mac in the inventory still on Monterey or Ventura.
In plain words:
- Building controllers. Who should care: anyone with a cold room, a heating system or badge doors serviced by an outside firm. Ask: "Can our controller be reached from the internet, and when was it last updated?" Technician: the attackers did not break in; they logged in to a web page that should not have been public. Orange Cyberdefense counted about 970 Danfoss and 123 Copeland systems reachable from the internet in the days after.
- WordPress. Who should care: anyone with a WordPress site, which is most small firms. Ask: "Is our site on 7.1.4?" Anyone on the internet can take the site over while it updates, no password needed. Technician: the flaw sits in the upgrade routine itself, so a site that failed its auto-update is the one to look at first.
- Cisco firewall. Who should care: anyone whose staff log in from home through a Cisco VPN with a second check. Ask: "Is our firewall on the fixed release, or did you switch the second check off?" The flaw knocks the firewall over, so everyone working from home drops off. Technician: a denial-of-service on the exploited list means someone is using it to take VPNs down, not to get in.
- Old Macs. Who should care: anyone with a Mac bought before 2021 still in daily use. Ask: "Which macOS is it on?" A two-year-old Safari flaw is being used now. Technician: Apple's note does not say exploited; CISA's list does. The fix is the OS, not the browser.
Ivanti, three weeks on. Two more Ivanti Connect Secure flaws, CVE-2026-111357 and CVE-2026-118527, went on CISA's exploited list on 30 October, chained with the one from week 42. Secondary sources name 22.8R2.6 and 25.1.1.3 as the fixed versions; Ivanti's own page would not load for us, so confirm there.
Four rows. Start with the freezer.
Get your weekly cyber to-do list
Every Thursday, a few steps for you, each with a date, and a list to forward to your IT partner. Two minutes, free, unsubscribe in one click.
Or use our RSS feed